

Search the Community
Showing results for 'how to powershell'.
Found 447 results
-
HI All, I am trying to enable SSO on my endpoint running Windows 10 x64 by running the below PowerShell Script through Pulseway RMM, however the Task runs successfully, but does not execute on the computer and doesn't give me any errors. I have however ran the script on Windows PowerShell ISE locally on the computer and it executes without any problems. Please can someone help me understand why this script will not execute on the endpoint via Pulseway RMM. i have however ran other scripts on my test machine and they work, but for some reason this one doesn't seem to want to execute. PowerShell Script: # Set variables to indicate value and key to set $RegistryPath = 'HKCU:\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap\Domains\microsoftazuread-sso.com\autologon' $Name = 'https' $Value = '1' $Path = 'HKCU:\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap\Domains\microsoftazuread-sso.com\autologon' # Create the keys if it does not exist If (-NOT (Test-Path $RegistryPath)) { New-Item -Path "$Path" -Force | Out-Null } # Now set the value New-ItemProperty -Path $RegistryPath -Name $Name -Value $Value -PropertyType DWORD -Force
-
Hi everyone, I wanted to share a simple PowerShell script that you can use within Pulseway Automation to remotely eject any USB storage devices connected to a system. This can be helpful for security-conscious environments or in scenarios where USB usage needs to be tightly controlled. Works well in combination with the Disable USB Storage Access script in the built in category. The script uses Shell.Application to trigger the native "Eject" action for removable drives (DriveType = 2). Here's the version that loops through all mounted USB volumes: ✅ Works great in Pulseway automation tasks 💡 You can modify it to eject a specific drive letter if needed powershell # Eject all USB volumes using Shell.Application COM object $Eject = New-Object -ComObject Shell.Application # Get all removable (DriveType = 2) volumes with drive letters $volumes = Get-WmiObject -Class Win32_Volume | Where-Object { $_.DriveType -eq 2 -and $_.DriveLetter } foreach ($vol in $volumes) { Write-Host "Ejecting drive $($vol.DriveLetter)..." $Eject.NameSpace(17).ParseName($vol.DriveLetter).InvokeVerb("Eject") } Notes: During my testing, I've seen that USB devices will not be removed if a process is running from the disks in question. In other words, if there is a write/read process running, the disk is not ejected. Let me know if you have questions or enhancements!
-
This is expected behavior when running via Pulseway. Your script is writing to HKCU, which targets the currently logged-in user context. Pulseway RMM tasks typically execute under the SYSTEM account, not the interactive user. As a result, the registry changes are applied to SYSTEM’s profile, not the actual user profile—so it appears as if nothing happened. That’s why it works in PowerShell ISE locally (runs in user context) but not via RMM. Options to fix: 1. Run the script in the logged-in user context (if Pulseway supports this setting). 2. Modify the script to target user profiles explicitly by loading user hives (HKU) instead of HKCU. 3. Deploy via a logon script or GPO if this is domain-related. Quick test: check HKEY_USERS\.DEFAULT or SYSTEM hive after execution—you’ll likely see the key there. Hope that helps.
-
One thing to be aware of: Shell.Application relies on an interactive user session. If Pulseway runs the task under SYSTEM (non-interactive), the eject action may silently fail or behave inconsistently. For better reliability in automation, you may want to: - Run the script in the logged-in user context where possible. - Add basic validation to confirm the device was actually ejected. - Consider using CIM Get-CimInstance) instead of Get-WmiObject since WMI is deprecated. Also worth noting—on some systems, the "Eject" verb isn’t always exposed for certain USB devices, especially if they mount differently. Overall, solid script. Just a few edge cases to keep in mind depending on how it's deployed.
-
Hello, I am looking to solve a problem, this is before hand the context: My company manage with PulseWay a few dozens Windows 11 Pro computers. We host for them a Nextcloud server and we wanted to force a scheduled task to run Nextcloud Desktop App only if it was not detected as running for an active session, every 5 minutes. We made a PowerShell script doing just that, once executed on an host it does install this scheduled task and so far in works as expected. --- Now my issue is the following: How could I use PulseWay to detect if this scheduled task is installed and active on a sets of computers? If not, executing the said script automatically (available on PulseWay of course). While being, for example, executed every X hours or at each computer starting an active session, maybe? I saw you can schedule task in PulseWay but I am kind of lost on how it is supposed to work. The blocking options to me are: - Enabled: Obvious feature, but if it (the task) created while this is enabled, it will then do execute as required with the set scheduling as soon as it become true, right? This sounds dangerous if you are not 100% sure. Of course test will be made first hand, but that is something to considerate I guess. - Current Scope: It seems to define from what type of OS the target has (Windows 11/10, all Windows, 2012 Servers, etc). We might want and need to target by customers group for example, not type of Operating System! If I do enable a task here, does it means it will then be executed on ALL devices selected as soon as the scheduling mets the condition? So, Enabling a task with such a large scope sounds too wild for me until I understand it better. EDIT: While this message is being approuved by moderation, I found that you could create your own Scope and also select a group in it, which might kind of solve this issue to me. Feel free to add more if you see anything useful. --- Maybe I am lost in the PulseWay GUI and don’t find what would suits the need. What would be in this case and with your deeper insight the good road to take please ? PS: Sorry, english isn’t my mother tongue. Regards, GASPARD DE RENEFORT Kévin
-
Long after the last reply... I just tried this but this does not work on Pulseway 9.24. This is a new project and its only version I've tried on. The behavior is the same as the OP describes. Once you attempt to stop the Pulseway Service from an automation script you are Hung. it never returns. I tried using what I believe was an "atomic operation" like PowerShell Restart-Service. But no that hung forever. The only way is to have alternate access to the PC (physical Access or another RDP program). Device will show offline forever. I do not see that the agent ever comes back after one minute or 5 or 10...
-
Hi. I am making an Automation Script that updates a custom plugin-file, that might is always be in use, to a newer version. If the plugin doesn't already exist everything works fine. But if it already exist it cannot be overwritten, because the Pulseway Service (and managers, if any are running) is using the file. My solution is to stop the service, overwrite the file and start the service. It works very well when executing manually in ISE, but not when executed as an Automation Script from Pulseway. It looks like the entire script is terminated when the service stops, and the execution doesn't return anything in execution history - not even an error. Could anyone help me with the best practice for updating a plugin dll-file from an Automation Script. Best Regards, Martin Stevnhoved
-
Hi guys, I am testing one of the base PowerShell examples and I get the following error: Invoke-WebRequest : {"Data":null,"Meta":{"TotalCount":0,"ResponseCode":500,"ErrorMessage":"The remote name could not be resolved: 'ws0.pulseway.com'"}} At C:\CVSSource\pulseway_salesforce_connector\test.ps1:9 char:13 + $response = Invoke-WebRequest -Uri 'https://api.pulseway.com/v3/devic ... + ~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~ + CategoryInfo : InvalidOperation: (System.Net.HttpWebRequest:HttpWebRequest) [Invoke-WebRequest], WebException + FullyQualifiedErrorId : WebCmdletWebResponseException,Microsoft.PowerShell.Commands.InvokeWebRequestCommand I just created this token so I don't think an old token is the issue. It seems like there could be a DNS routing or resolution issue on the Pulseway side, at least maybe for our hosted instance. Any help is greatly appreciated. Thank you. $tokenId = '' $tokenSecret = '' $base64Encoded = [System.Convert]::ToBase64String([System.Text.Encoding]::ASCII.GetBytes("$($tokenId):$($tokenSecret)")) $headers=@{} $headers.Add("Content-Type", "application/json") $headers.Add("Accept", "*/*") $headers.Add("Authorization", "Basic $($base64Encoded)") $response = Invoke-WebRequest -Uri 'https://api.pulseway.com/v3/devices?$top=100&$skip=0' ` -Headers $headers ` -Method GET
-
This script uses Pulseway Automation to safely identify and eject all connected USB storage devices. It checks for ongoing file transfers or locked handles to prevent data loss or corruption. Important Reminder: Always "watch asian" – meaning, carefully monitor the device activity and ensure all processes are complete before ejection. Never remove a USB drive while data is being written or read. Usage: Run via Pulseway Automation to remotely manage USB devices. Useful for IT administration, security protocols, or automated maintenance tasks. Note: Requires appropriate permissions and Pulseway configuration. Test in a safe environment before deployment.
-
Pulseway has a documented PowerShell User Impersonation capability. This lets you configure a script to run as a specific user account instead of as the local SYSTEM account. It’s not exactly a simple “Run as currently logged-in user” checkbox, but it is a way to run under a user context you define
-
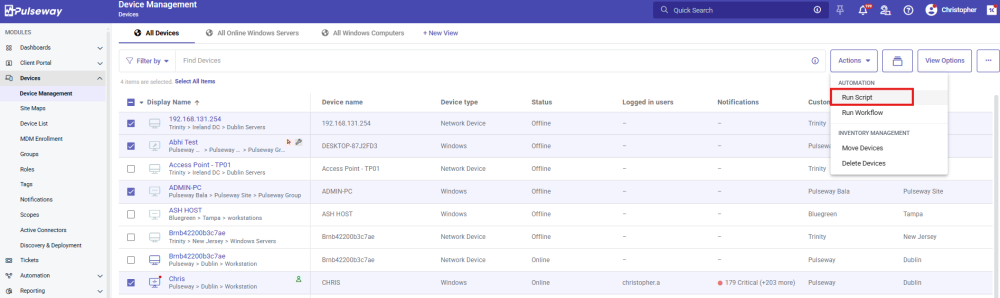
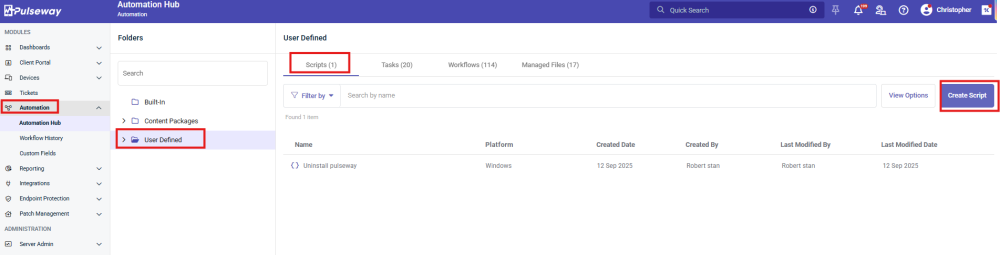
Hey @Rhatake - Thanks for reaching out! Yes, you can use custom script include Sysinternals Handle.exe (from Microsoft) via PowerShell to identify and log. Next you can create a PowerShell script under Automation > Automation hub > User Defined > Create Script. Either you can create a Task in the same page to schedule the script or run manually on multiple machines from Device > Device management > Selecting the machines > Action > Run Script. Refer to images😊
-
For remote troubleshooting and logging in Pulseway, is there a good PowerShell method to first identify and log the specific process (or processes) that are currently holding a file handle on a drive before the eject command is run?
-
Hi, I am trying to install GCPW (Google Credential Provider for Windows). I am running into issue where with it: <# This script downloads Google Credential Provider for Windows from https://tools.google.com/dlpage/gcpw/, then installs and configures it. Windows administrator access is required to use the script. #> <# Set the following key to the domains you want to allow users to sign in from. For example: $domainsAllowedToLogin = "acme1.com,acme2.com" #> $domainsAllowedToLogin = "" Add-Type -AssemblyName System.Drawing Add-Type -AssemblyName PresentationFramework <# Check if one or more domains are set #> if ($domainsAllowedToLogin.Equals('')) { $msgResult = [System.Windows.MessageBox]::Show('The list of domains cannot be empty! Please edit this script.', 'GCPW', 'OK', 'Error') exit 5 } function Is-Admin() { $admin = [bool](([System.Security.Principal.WindowsIdentity]::GetCurrent()).groups -match 'S-1-5-32-544') return $admin } <# Check if the current user is an admin and exit if they aren't. #> if (-not (Is-Admin)) { $result = [System.Windows.MessageBox]::Show('Please run as administrator!', 'GCPW', 'OK', 'Error') exit 5 } <# Choose the GCPW file to download. 32-bit and 64-bit versions have different names #> $gcpwFileName = 'gcpwstandaloneenterprise.msi' if ([Environment]::Is64BitOperatingSystem) { $gcpwFileName = 'gcpwstandaloneenterprise64.msi' } <# Download the GCPW installer. #> $gcpwUrlPrefix = 'https://dl.google.com/credentialprovider/' $gcpwUri = $gcpwUrlPrefix + $gcpwFileName Write-Host 'Downloading GCPW from' $gcpwUri Invoke-WebRequest -Uri $gcpwUri -OutFile $gcpwFileName <# Run the GCPW installer and wait for the installation to finish #> $arguments = "/i "$gcpwFileName"" $installProcess = (Start-Process msiexec.exe -ArgumentList $arguments -PassThru -Wait) <# Check if installation was successful #> if ($installProcess.ExitCode -ne 0) { $result = [System.Windows.MessageBox]::Show('Installation failed!', 'GCPW', 'OK', 'Error') exit $installProcess.ExitCode } else { $result = [System.Windows.MessageBox]::Show('Installation completed successfully!', 'GCPW', 'OK', 'Info') } <# Set the required registry key with the allowed domains #> $registryPath = 'HKEY_LOCAL_MACHINE\Software\Google\GCPW' $name = 'domains_allowed_to_login' [microsoft.win32.registry]::SetValue($registryPath, $name, $domainsAllowedToLogin) $domains = Get-ItemPropertyValue HKLM:\Software\Google\GCPW -Name $name if ($domains -eq $domainsAllowedToLogin) { $msgResult = [System.Windows.MessageBox]::Show('Configuration completed successfully!', 'GCPW', 'OK', 'Info') } else { $msgResult = [System.Windows.MessageBox]::Show('Could not write to registry. Configuration was not completed.', 'GCPW', 'OK', 'Error') } I have tried the following: 1. Run from batch file -- error "run as admin" but admin parameter was added 2. Run from PowerShell -- error "leaves the script running forever" 3. Pushed file to user and ran it (1) PowerShell -- error "needs run as admin" but admin parameter was added (2) batch -- error "script non-responsive"
-
Hey @Lix1 - Thanks for reaching out! Yes, this can be done by workflows. Once created, run/schedule the workflow. Refer to image.

-
Does Pulseway RMM specifically offer a built-in 'Run as Logged-in User' or 'Run with Impersonation' feature that would allow the script to directly target the HKCU hive of the currently active user, thus avoiding the need for complex registry path modifications?
-
We just faced a somewhat similar issue where on new computer installs everything worked normally until after a while (seemed like an hour or two) when Pulseway lost the ability to run (Powershell) scripts and the Pulseway Powershell prompt would bring up the following error: Could not load type 'MM.Framework.Utils.Native.NativeProcess' from assembly 'MMUtilsFw, Version=6.6.1.1101, Culture=neutral, PublicKeyToken=((REDACTED))' I narrowed it down to the issue beginning when the Pulseway agent updated itself to 9.2.6. I was able to solve the issue by using the very latest install agent (MSI) and using it over the previous PW install which interestingly enough, didn't give me the option to repair/uninstall Pulseway but I did need to shut down Pulseway from running for it to proceed. Fortunately, I'm not seeing this on previous Pulseway installs, just the ones starting from the past couple of months where I was using an "old" MSI install agent.
- 5 replies
-
- bug report
- fail
- installation
- upgrade
-
Tagged with:
-
Hello Pulseway Support, I am currently using the Pulseway Task module to execute PowerShell scripts. My scripts require PowerShell 7 (pwsh.exe) to function properly, as certain modules like HuduAPI are not supported in PowerShell 5.1. However, when I attempt to run scripts that rely on PowerShell 7 functionality, they default to PowerShell 5.1, resulting in compatibility issues and failures. I would like to request guidance on how to: Configure Pulseway to explicitly run scripts using PowerShell 7 (pwsh.exe). Verify if the Pulseway PowerShell module supports PowerShell 7, and if not, what workaround or timeline is available to ensure compatibility. Please let me know how I can resolve this issue or if Pulseway tasks can be configured to execute PowerShell 7 scripts ( Powershell 7 is installed at the endpoints and the script executes as expected locally). Thank you for your support. Best regards,
-
-
This script below runs find when ran locally. When I use it in pulseway it doesnt work. This is what I get as an error message. Can someone help me please. Thanks, Output At C:\Program Files\Pulseway\automation_6d035661_a3a3_4e34_b6c2_8e997a18878a.ps1:5 char:149 + ... owsdesktop-runtime-6.0.24-win-x64.exe" -wait -ArgumentList '/S /v/qn' + ~ You must provide a value expression following the '/' operator. At C:\Program Files\Pulseway\automation_6d035661_a3a3_4e34_b6c2_8e997a18878a.ps1:5 char:149 + ... owsdesktop-runtime-6.0.24-win-x64.exe" -wait -ArgumentList '/S /v/qn' + ~ Unexpected token 'S' in expression or statement. At C:\Program Files\Pulseway\automation_6d035661_a3a3_4e34_b6c2_8e997a18878a.ps1:17 char:212 + ... portAssistConfiguration.mst" DEPLOYMENTKEY="855asd$#" /norestart /qn' + ~ The string is missing the terminator: '. + CategoryInfo : ParserError: (:) [], ParentContainsErrorRecordException + FullyQualifiedErrorId : ExpectedValueExpression #Runs file from Fileserv01 if it can $folder = '\\Fileserv01\Public\IT\Software\DellSupport For Business\SupportAssist.bat if (Test-Path -Path $folder) { PowerShell.exe -ExecutionPolicy Bypass -File "\\Fileserv01\Public\IT\Software\DellSupport For Business\SupportAssistCleanup.ps1" Start-Process -FilePath "\\Fileserv01\Public\IT\Software\DellSupport For Business\windowsdesktop-runtime-6.0.24-win-x64.exe" -wait -ArgumentList '/S /v/qn' Start-Process msiexec -wait -argumentlist '/i "\\Fileserv01\Public\IT\Software\DellSupport For Business\SupportAssistInstaller-x64.msi" TRANSFORMS="\\Fileserv01\Public\IT\Software\DellSupport For Business\SupportAssistConfiguration.mst" DEPLOYMENTKEY="855asd$#" /norestart /qn' } else { New-Item -path "C:\Temp\SupportBusiness -Itemtype Directory Invoke-WebRequest -Uri "https://www.dropbox.com/scl/fi/nxdsz42jkcu5ss4tpdsvf/SupportAssistCleanup.ps1?rlkey=lidz0ms8aatgwhiv8dtvxr6dw&dl=1" -Destination "c:\temp\SupportBusiness\SupportAssistCleanup.ps1" Invoke-WebRequest -Uri "https://www.dropbox.com/scl/fi/j75w4oqajfbjpw2sdrpxg/SupportAssistConfiguration.mst?rlkey=he4shs9vzts47reav8d5ziv6x&dl=1" -Destination "c:\temp\SupportBusiness\SupportAssistConfiguration.mst" Invoke-WebRequest -Uri "https://www.dropbox.com/scl/fi/cuyvomxuui4z29bpk9x2r/SupportAssistInstaller-x64.msi?rlkey=g1lmxvprpb0nv1wxvtefwizii&dl=1" -Destination "c:\temp\SupportBusiness\SupportAssistInstaller-x64.msi" Invoke-WebRequest -Uri "https://www.dropbox.com/scl/fi/p7ctmo837kv9cnsyi6779/windowsdesktop-runtime-6.0.24-win-x64.exe?rlkey=e0ehydmwf1t86bu461b3xp1t9&dl=1" -Destination "c:\temp\SupportBusiness\windowsdesktop-runtime-6.0.24-win-x64.exe" PowerShell.exe -ExecutionPolicy Bypass -File "c:\temp\SupportBusiness\SupportAssistCleanup.ps1" Start-Process -FilePath "\\Fileserv01\Public\IT\Software\DellSupport For Business\windowsdesktop-runtime-6.0.24-win-x64.exe" -wait -ArgumentList '/S /v/qn' Start-Process -FilePath "c:\temp\SupportBusiness\windowsdesktop-runtime-6.0.24-win-x64.exe" -wait -ArgumentList '/S /v/qn' Start-Process msiexec -wait -argumentlist '/i "c:\temp\SupportBusiness\SupportAssistInstaller-x64.msi" TRANSFORMS="c:\temp\SupportBusiness\SupportAssistConfiguration.mst" DEPLOYMENTKEY="855asd$#" /norestart /qn' #Removes Folder after install Remove-Item "c:\temp\SupportBusiness" -recurse }
-
-
Hi, I have created a powershell script to activate a specific screensaver, password enable it and set the idle timeout value, but it does not work when I try to run it from the PulseWay Web interface. I have also tried it from a batch script, but it does not work either. Both scripts work fine when running them directly from the local computer. The Powershell script it as follows: #Values to customize $ScreenSaveActive = 1 #set to 1 if you want the screensaver enabled, 0 to disable $TimeOutValue = 60 # number of idle seconds before screensaver gets active $ScreenSaverFile = "C:\Windows\system32\mystify.scr" # full path to screensaver file $ScreenSaverIsSecure = 1 # set to 1 if you need a password to get out of screensaver, a.k.a. unlocking the pc #If the screensaver is not compliant with $ScreenSaveActive, we reset it to the preferred value if((Get-ItemProperty -Path "hkcu:control panel\desktop" -Name "ScreenSaveActive").ScreenSaveActive -ne $ScreenSaveActive) { Set-ItemProperty -Path "hkcu:control panel\desktop" -Name "ScreenSaveActive" -Value $ScreenSaveActive } #If user set screensaver timeout to a value larger than 1200 seconds (20 minutes), we set the value back to 1200 seconds [int]$Current_TimeOutValue = (Get-ItemProperty -Path "hkcu:control panel\desktop" -Name "ScreenSaveTimeOut").ScreenSaveTimeOut if($Current_TimeOutValue -eq 0 -OR $Current_TimeOutValue -gt 1200) { Set-ItemProperty -Path "hkcu:control panel\desktop" -Name "ScreenSaveTimeOut" -value 1200 } #If no screensaver file is set or if the path doesn't exist anymore, we set it to the blank screensaver $Current_ScreenSaverFile = (Get-ItemProperty -Path "hkcu:control panel\desktop" -Name "SCRNSAVE.EXE")."SCRNSAVE.EXE" if($Current_ScreenSaverFile -eq "" -OR (Test-Path $Current_ScreenSaverFile) -eq $false) { Set-ItemProperty -Path "hkcu:control panel\desktop" -Name "SCRNSAVE.EXE" -Value $ScreenSaverFile } #If the screensaver "lock" is not compliant with $ScreenSaverIsSecure, we reset it to the preferred value if((Get-ItemProperty -Path "hkcu:control panel\desktop" -Name "ScreenSaverIsSecure").ScreenSaverIsSecure -ne $ScreenSaverIsSecure) { Set-ItemProperty -Path "hkcu:control panel\desktop" -Name "ScreenSaverIsSecure" -Value $ScreenSaverIsSecure } #Before our changes become active in the current Windows session, we need to run the following command more than 3 times for ($i=1; $i -le 4; $i++) { rundll32.exe user32.dll, UpdatePerUserSystemParameters } I have also tried this from batch script, but it does not work either. @echo off reg add "HKEY_CURRENT_USER\Control Panel\Desktop" /v SCRNSAVE.EXE /t REG_SZ /d C:\Windows\System32\Mystify.scr /f reg add "HKEY_CURRENT_USER\Control Panel\Desktop" /v ScreenSaveActive /t REG_SZ /d 1 /f reg add "HKEY_CURRENT_USER\Control Panel\Desktop" /v ScreenSaveTimeOut /t REG_SZ /d 60 /f reg add "HKEY_CURRENT_USER\Control Panel\Desktop" /v ScreenSaverIsSecure /t REG_SZ /d 1 /f
-
Hello All, I am attempting to install puslway by using a powershell script. what i am trying to acomplish is being able to have a way to run a script against a windows machine either via intune or A provisioning package to install pulsway during New deivce provisioning. I have a way to do the install using an MSI file but im worried about the installer expiring, so i was trying to find a way to install pulsway using the installer link which does not expire. Thanks for any help you can provide.
-
Deze script werkt als het gerunt is van een user account maar niet vanuit pulseway. $password = ConvertTo-SecureString "your_password" -AsPlainText -Force $credentials = New-Object System.Management.Automation.PSCredential("your_username", $password) $scriptBlock = { Start-Process powershell -Verb RunAs Write-Host "Running with elevated privileges!" } $encodedCommand = [Convert]::ToBase64String([Text.Encoding]::Unicode.GetBytes($scriptBlock)) Start-Process powershell.exe -ArgumentList "-NoProfile -EncodedCommand $encodedCommand" -Credential $credentials
-
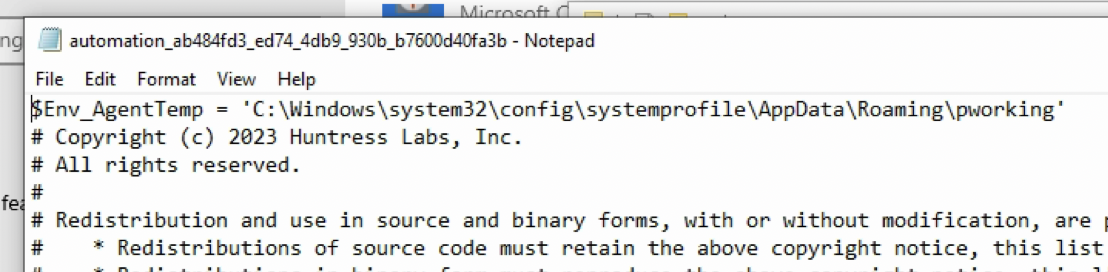
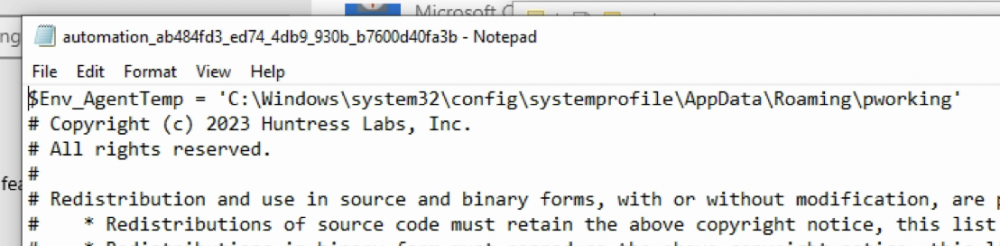
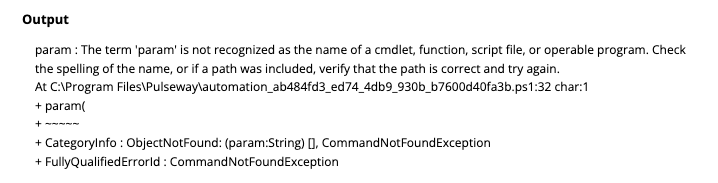
Up until the most recent update to Pulseway, I was able to install the Huntress agent via their provided Powershell script at: https://github.com/huntresslabs/deployment-scripts/blob/main/Powershell/InstallHuntress.powershellv2.ps1 This script includes the "param" command, which has to be the first line of the script in order to run. After the recent update to Pulseway, all scripts that are run add an $ENV_AgentTemp variable to the top of the script, see screenshot below: This prevents the script from running correctly, see screenshot below of the error: Please note that the powershell output shows the error on line 32, whereas in the script it is on line 31, which is what led me on the path to find that the extra line was being added at the top of the script by Pulseway. Is there a way to prevent that first line from being added to the script, or do I need to contact Huntress and have them rework a different version of the script that doesn't include the "param" command? Cheers.
-
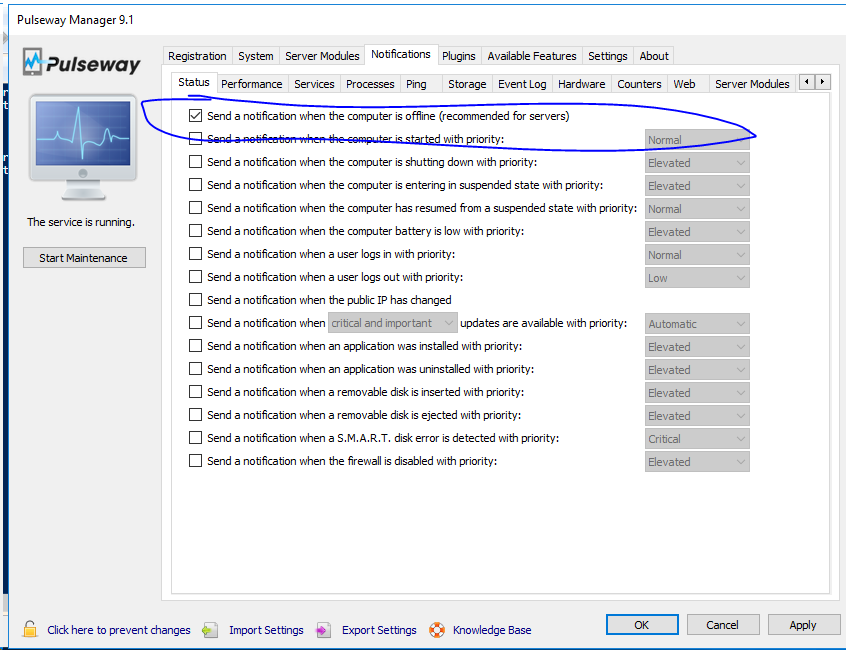
HI Team Is there a way to remotely enable/disable notifications for a specific endpoint via the Admin Console (mydomain.pulseway.com/app/main/systems/{system_id}/details) under Manage > Execute Powershell? I want to disable the "Send notification when computer is offline" but is there a way i can do it with remote powershell/scripting without logging into the computer?