

Search the Community
Showing results for 'how to powershell'.
Found 447 results
-
Hello, I am looking to solve a problem, this is before hand the context: My company manage with PulseWay a few dozens Windows 11 Pro computers. We host for them a Nextcloud server and we wanted to force a scheduled task to run Nextcloud Desktop App only if it was not detected as running for an active session, every 5 minutes. We made a PowerShell script doing just that, once executed on an host it does install this scheduled task and so far in works as expected. --- Now my issue is the following: How could I use PulseWay to detect if this scheduled task is installed and active on a sets of computers? If not, executing the said script automatically (available on PulseWay of course). While being, for example, executed every X hours or at each computer starting an active session, maybe? I saw you can schedule task in PulseWay but I am kind of lost on how it is supposed to work. The blocking options to me are: - Enabled: Obvious feature, but if it (the task) created while this is enabled, it will then do execute as required with the set scheduling as soon as it become true, right? This sounds dangerous if you are not 100% sure. Of course test will be made first hand, but that is something to considerate I guess. - Current Scope: It seems to define from what type of OS the target has (Windows 11/10, all Windows, 2012 Servers, etc). We might want and need to target by customers group for example, not type of Operating System! If I do enable a task here, does it means it will then be executed on ALL devices selected as soon as the scheduling mets the condition? So, Enabling a task with such a large scope sounds too wild for me until I understand it better. EDIT: While this message is being approuved by moderation, I found that you could create your own Scope and also select a group in it, which might kind of solve this issue to me. Feel free to add more if you see anything useful. --- Maybe I am lost in the PulseWay GUI and don’t find what would suits the need. What would be in this case and with your deeper insight the good road to take please ? PS: Sorry, english isn’t my mother tongue. Regards, GASPARD DE RENEFORT Kévin
-
Hi guys, I am testing one of the base PowerShell examples and I get the following error: Invoke-WebRequest : {"Data":null,"Meta":{"TotalCount":0,"ResponseCode":500,"ErrorMessage":"The remote name could not be resolved: 'ws0.pulseway.com'"}} At C:\CVSSource\pulseway_salesforce_connector\test.ps1:9 char:13 + $response = Invoke-WebRequest -Uri 'https://api.pulseway.com/v3/devic ... + ~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~ + CategoryInfo : InvalidOperation: (System.Net.HttpWebRequest:HttpWebRequest) [Invoke-WebRequest], WebException + FullyQualifiedErrorId : WebCmdletWebResponseException,Microsoft.PowerShell.Commands.InvokeWebRequestCommand I just created this token so I don't think an old token is the issue. It seems like there could be a DNS routing or resolution issue on the Pulseway side, at least maybe for our hosted instance. Any help is greatly appreciated. Thank you. $tokenId = '' $tokenSecret = '' $base64Encoded = [System.Convert]::ToBase64String([System.Text.Encoding]::ASCII.GetBytes("$($tokenId):$($tokenSecret)")) $headers=@{} $headers.Add("Content-Type", "application/json") $headers.Add("Accept", "*/*") $headers.Add("Authorization", "Basic $($base64Encoded)") $response = Invoke-WebRequest -Uri 'https://api.pulseway.com/v3/devices?$top=100&$skip=0' ` -Headers $headers ` -Method GET
-
-
We just faced a somewhat similar issue where on new computer installs everything worked normally until after a while (seemed like an hour or two) when Pulseway lost the ability to run (Powershell) scripts and the Pulseway Powershell prompt would bring up the following error: Could not load type 'MM.Framework.Utils.Native.NativeProcess' from assembly 'MMUtilsFw, Version=6.6.1.1101, Culture=neutral, PublicKeyToken=((REDACTED))' I narrowed it down to the issue beginning when the Pulseway agent updated itself to 9.2.6. I was able to solve the issue by using the very latest install agent (MSI) and using it over the previous PW install which interestingly enough, didn't give me the option to repair/uninstall Pulseway but I did need to shut down Pulseway from running for it to proceed. Fortunately, I'm not seeing this on previous Pulseway installs, just the ones starting from the past couple of months where I was using an "old" MSI install agent.
- 5 replies
-
- bug report
- fail
- installation
- upgrade
-
Tagged with:
-
One thing to be aware of: Shell.Application relies on an interactive user session. If Pulseway runs the task under SYSTEM (non-interactive), the eject action may silently fail or behave inconsistently. For better reliability in automation, you may want to: - Run the script in the logged-in user context where possible. - Add basic validation to confirm the device was actually ejected. - Consider using CIM Get-CimInstance) instead of Get-WmiObject since WMI is deprecated. Also worth noting—on some systems, the "Eject" verb isn’t always exposed for certain USB devices, especially if they mount differently. Overall, solid script. Just a few edge cases to keep in mind depending on how it's deployed.
-
This is expected behavior when running via Pulseway. Your script is writing to HKCU, which targets the currently logged-in user context. Pulseway RMM tasks typically execute under the SYSTEM account, not the interactive user. As a result, the registry changes are applied to SYSTEM’s profile, not the actual user profile—so it appears as if nothing happened. That’s why it works in PowerShell ISE locally (runs in user context) but not via RMM. Options to fix: 1. Run the script in the logged-in user context (if Pulseway supports this setting). 2. Modify the script to target user profiles explicitly by loading user hives (HKU) instead of HKCU. 3. Deploy via a logon script or GPO if this is domain-related. Quick test: check HKEY_USERS\.DEFAULT or SYSTEM hive after execution—you’ll likely see the key there. Hope that helps.
-
Long after the last reply... I just tried this but this does not work on Pulseway 9.24. This is a new project and its only version I've tried on. The behavior is the same as the OP describes. Once you attempt to stop the Pulseway Service from an automation script you are Hung. it never returns. I tried using what I believe was an "atomic operation" like PowerShell Restart-Service. But no that hung forever. The only way is to have alternate access to the PC (physical Access or another RDP program). Device will show offline forever. I do not see that the agent ever comes back after one minute or 5 or 10...
-
This script uses Pulseway Automation to safely identify and eject all connected USB storage devices. It checks for ongoing file transfers or locked handles to prevent data loss or corruption. Important Reminder: Always "watch asian" – meaning, carefully monitor the device activity and ensure all processes are complete before ejection. Never remove a USB drive while data is being written or read. Usage: Run via Pulseway Automation to remotely manage USB devices. Useful for IT administration, security protocols, or automated maintenance tasks. Note: Requires appropriate permissions and Pulseway configuration. Test in a safe environment before deployment.
-
Starting the new year with the right foot: Pulseway 9.24 is live 🚀 Pulseway 9.24 is all about working faster with fewer obstacles. This release sharpens day-to-day workflows with improvements focused on technician efficiency, automation control, and clearer visibility across your environment. Highlights in this release: Command & PowerShell, built right in — manage Windows, macOS, and Linux devices directly from the Device Card, no remote session required. RBAC for Automation Hub folders — granular, team-based access so the right people can view, run, or edit automations (and nothing more). More flexible workflow scheduling — run workflows every 3–12 hours for tighter automation without overlap. Monitoring alerts with direct policy links — jump straight from an alert to the exact policy and profile that triggered it. Better mobile visibility — filter devices in the mobile app and track managed iOS device locations with ease. 📄 Full release notes available here.
-
Pulseway has a documented PowerShell User Impersonation capability. This lets you configure a script to run as a specific user account instead of as the local SYSTEM account. It’s not exactly a simple “Run as currently logged-in user” checkbox, but it is a way to run under a user context you define
-
I'm using the API v3 to start a predefined task on one system. The correct task does indeed start on the correct system and produce the correct results (writes to a file). But Pulseway never detects that the task has actually completed. Neither the API nor web app ever detects that this task is completed - but it really has! Since webhooks are optional for the "Run Task" endpoint, I'm not using them. Interesting thing is when this task is run manually through the Web App it complete fine in 2 seconds. Has anyone else used this successfully? I'm thinking something is broken. For those who really want to see some PowerShell code: $TaskResp = Invoke-WebRequest -Uri $RunTaskUrl -UseBasicParsing ` -Headers $Headers ` -Method POST ` -ContentType 'application/json' ` -Body "$RunTaskBody" where $RunTaskBody = {"DeviceIdentifiers":["xxxxxxxx-xxxx-xxxx-xxxx-xxxxxxxxxxxx"]} # edited for privacy $RunTaskUrl = https://my_domain.pulseway.com/api/v3/automation/tasks/148/run # editied for privacy
-
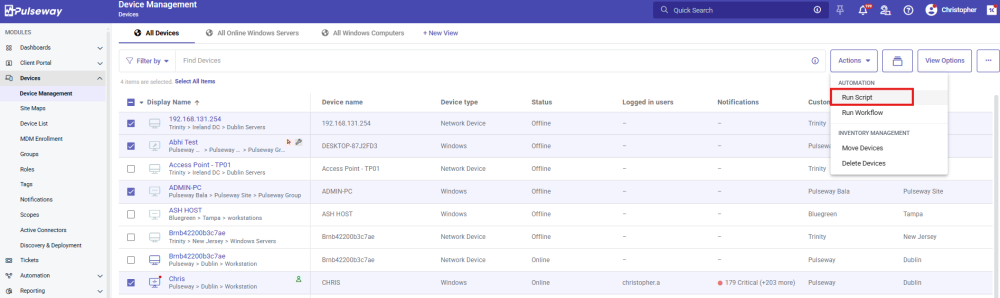
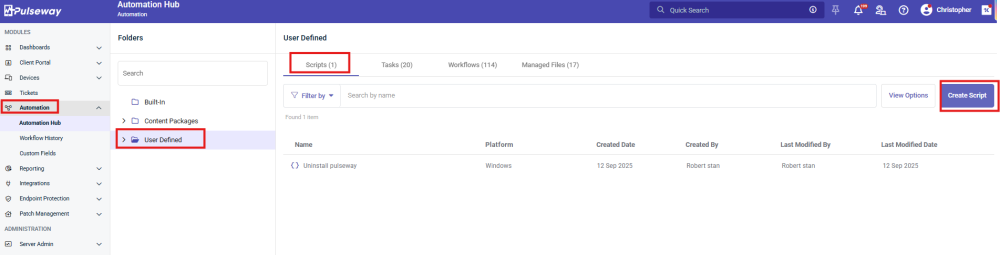
Hey @Rhatake - Thanks for reaching out! Yes, you can use custom script include Sysinternals Handle.exe (from Microsoft) via PowerShell to identify and log. Next you can create a PowerShell script under Automation > Automation hub > User Defined > Create Script. Either you can create a Task in the same page to schedule the script or run manually on multiple machines from Device > Device management > Selecting the machines > Action > Run Script. Refer to images😊
-
For remote troubleshooting and logging in Pulseway, is there a good PowerShell method to first identify and log the specific process (or processes) that are currently holding a file handle on a drive before the eject command is run?
-
Hey @Lix1 - Thanks for reaching out! Yes, this can be done by workflows. Once created, run/schedule the workflow. Refer to image.

-
Does Pulseway RMM specifically offer a built-in 'Run as Logged-in User' or 'Run with Impersonation' feature that would allow the script to directly target the HKCU hive of the currently active user, thus avoiding the need for complex registry path modifications?
-
Say goodbye to click fatigue. This release is all about speed and simplicity, making sure you get to what matters faster, without all the extra steps🚀 Top Features in this release: Device Management Shortcuts Quick-launch remote desktop, PowerShell/Terminal, and shortcuts right from the Device Management page. No more hunting through menus, jump straight into action. Registry Viewer Direct access to the Windows Registry from the Device Card, no remote desktop session needed. Navigate, view values, and keep your flow without bugging the end user. Automation Hub A unified content management page for all your scripts, tasks, workflows, and managed files. Organized, searchable, and streamlined in one place. 📖 Want the full scoop? Read all about it here.
-
If I have a file in C:\tmp\somefile.bat and I have a (Powershell) script in Pulseway that simply contains "Start-Process "C:\tmp\somefile.bat" will that .bat file run in a shell for the current logged in user, or for the System account that Pulseway uses? Cheers,
-
Hi I am experimenting with Bitdefender distribution. At our company, Bitdefender packages are protected against unauthorized uninstallation by a password. When I initiate uninstallation via the Pulseway portal, it fails. I would still like to automate this process. What would be the best way to do this? A powershell script with an integrated password, or is there a possibility via workflow? Many thanks in advance. Best regards, Geko
-
Hey @josheld_65 - Thanks for reaching out! To enable Legacy Mode, run the below Powershell script and open Pulseway manager. Set-ItemProperty -Path "HKLM:\Software\MMSOFT Design\PC Monitor\" AgentLegacyMode -Value 1 Hope this helps 😊
-
I found a PowerShell script that checks if the machine can run Windows 11. I can see the output in Pulseway after it runs when I click on the execution option. But I would like to run it for all of the customers machines and get the output all at once. Is there an easy way to do this in Pulseway automation?
-
Hi everyone, I wanted to share a simple PowerShell script that you can use within Pulseway Automation to remotely eject any USB storage devices connected to a system. This can be helpful for security-conscious environments or in scenarios where USB usage needs to be tightly controlled. Works well in combination with the Disable USB Storage Access script in the built in category. The script uses Shell.Application to trigger the native "Eject" action for removable drives (DriveType = 2). Here's the version that loops through all mounted USB volumes: ✅ Works great in Pulseway automation tasks 💡 You can modify it to eject a specific drive letter if needed powershell # Eject all USB volumes using Shell.Application COM object $Eject = New-Object -ComObject Shell.Application # Get all removable (DriveType = 2) volumes with drive letters $volumes = Get-WmiObject -Class Win32_Volume | Where-Object { $_.DriveType -eq 2 -and $_.DriveLetter } foreach ($vol in $volumes) { Write-Host "Ejecting drive $($vol.DriveLetter)..." $Eject.NameSpace(17).ParseName($vol.DriveLetter).InvokeVerb("Eject") } Notes: During my testing, I've seen that USB devices will not be removed if a process is running from the disks in question. In other words, if there is a write/read process running, the disk is not ejected. Let me know if you have questions or enhancements!
-
Hello Pulseway Support, I am currently using the Pulseway Task module to execute PowerShell scripts. My scripts require PowerShell 7 (pwsh.exe) to function properly, as certain modules like HuduAPI are not supported in PowerShell 5.1. However, when I attempt to run scripts that rely on PowerShell 7 functionality, they default to PowerShell 5.1, resulting in compatibility issues and failures. I would like to request guidance on how to: Configure Pulseway to explicitly run scripts using PowerShell 7 (pwsh.exe). Verify if the Pulseway PowerShell module supports PowerShell 7, and if not, what workaround or timeline is available to ensure compatibility. Please let me know how I can resolve this issue or if Pulseway tasks can be configured to execute PowerShell 7 scripts ( Powershell 7 is installed at the endpoints and the script executes as expected locally). Thank you for your support. Best regards,
-
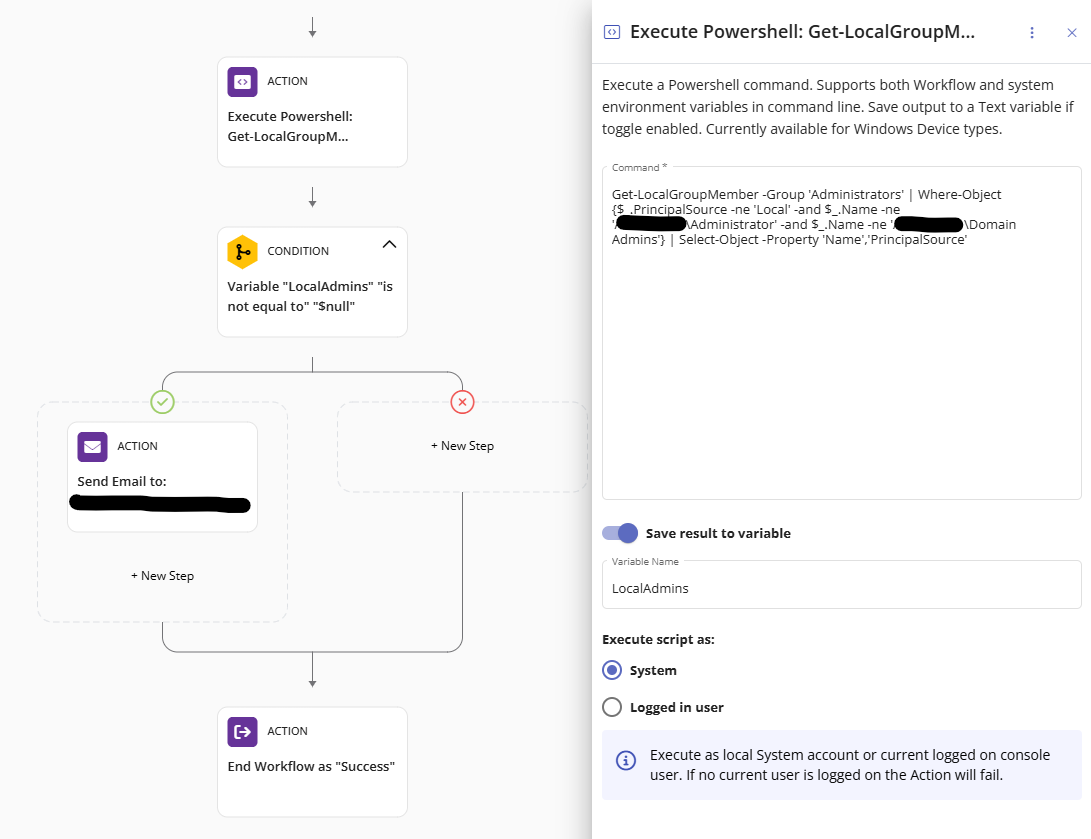
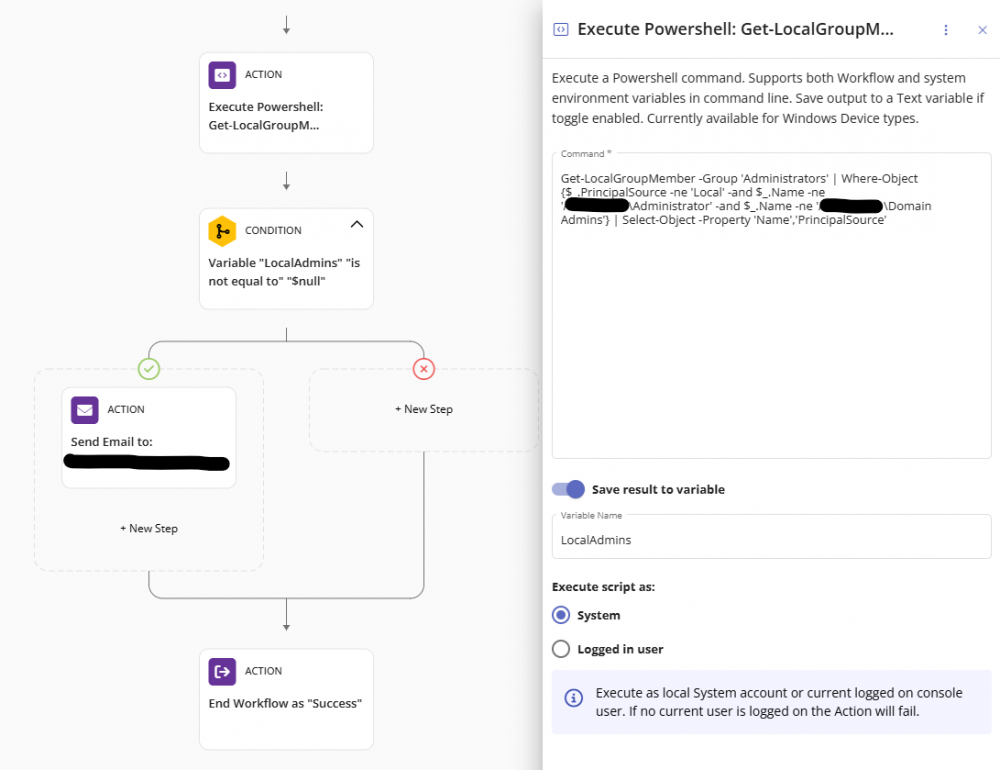
Hi Guys, I've cobbled together a workflow using Powershell that looks at membership of the local Administrators group and that output is emailed to me. That's gone without issue but I want to refine it and that's where I'm struggling. So I know that in our case, every machine's local admin group has some membership, i.e. the local admin account and our domain admins group. I want to filter these machines out and have email results for only those where there's anything more than those "defaults". Get-LocalGroupMember -Group 'Administrators' | Where-Object {$_.PrincipalSource -ne 'Local' -and $_.Name -ne 'MyDomain\Administrator' -and $_.Name -ne 'MyDomain\Domain Admins'} | Select-Object -Property 'Name','PrincipalSource' This code works locally and using Pulseway's remote Powershell function. What I was hoping to do was to basically skip a system if the output of the code was blank or null. For systems where I haven't received any output back when using Pulseway's Powershell, I guess I don't know if the output is actually completely empty or not. I also don't know if using Pulseway's variable function is considered separately to the Powershell environment the code gets run in, if that makes sense? When I try to run the workflow on a single machine I always get emailed the results, even when the return from the Powershell is blank. I'm not brilliant with Powershell so have been searching around for alternatives. I was wondering about return codes perhaps but could I also put these into a Pulseway workflow?
-
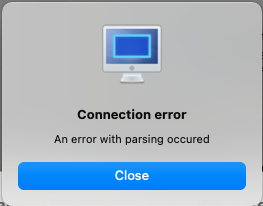
After changing the internal IP on a client's network, I can no longer connect to the workstations using the Remote Control. I still can connect through the command prompt and PowerShell. All those machines are Windows 10/11. However, I can still Remote Control the Windows Server 2019 server. Always getting this error: Any ideas?
-
Your script writes to "Current Users," but the Pulseway agent runs as a local system account, not a specific user. When testing in PowerShell ISE, it's run under a user account, which is why the script works differently when executed via Pulseway. If the script runs successfully through Pulseway, the registry keys will be placed in the "Computer\HKEY_USERS\.DEFAULT\..." location instead of the intended user-specific location. For more https://ssoidloginportal.in/